Most advice about model context protocol for business treats it as the thing to adopt: install a server, connect your tools, and the AI starts doing real work. That skips the part that decides whether anything works.
MCP is a useful connection standard. It does not tell you which process to automate, what the assistant may touch, who approves what, or who notices when it breaks. That surrounding work is where the value is, and for some companies it means MCP can wait.
Here is what the protocol does, how it differs from what you already have, and how to decide whether to build, buy or wait.
What is Model Context Protocol in business terms?
Model Context Protocol (MCP) is an open standard, introduced by Anthropic at the end of 2024, that lets AI assistants use business tools and data through one shared interface. Instead of a custom connection for every pairing of model and system, each tool exposes itself once in a common format the assistant can read.
Three roles matter. The host is the application that embeds the AI agent. The client handles communication between the agent and the tool. The server is where the tool lives, such as a CRM or a knowledge base.
A server can expose three things: tools (functions the assistant can run), prompts (prewritten templates) and resources (files, logs, tables and other data). OpenAI publicly adopted MCP in March 2025, so it is not tied to one model vendor.
What problem does MCP solve for a business running AI?
Without a standard, every assistant-to-tool link is a one-off build. Say you want an assistant to read a customer record in your CRM and open a ticket in your help desk. That is two custom integrations, and a third if you switch models.
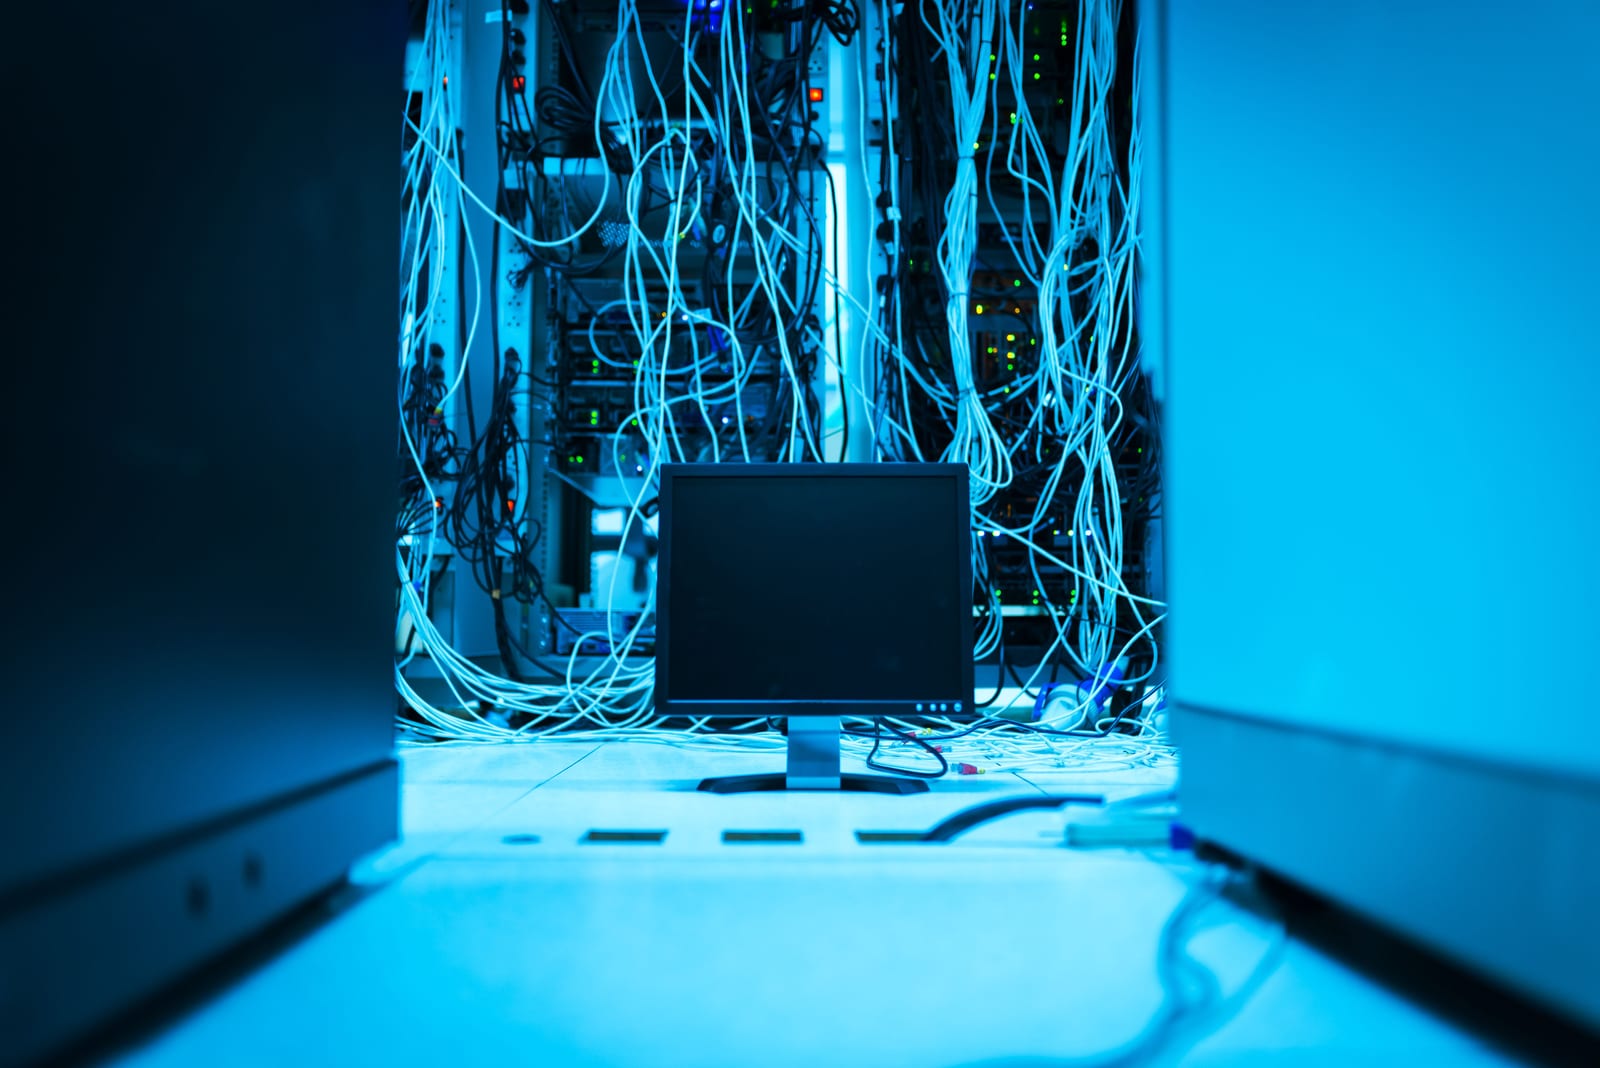
Every one-off connection is another cable someone has to understand, maintain and fix when it quietly breaks.
Those links break quietly when an app changes a field name or an endpoint. Each one has its own authentication, its own error behavior and, usually, one person who understands it.
MCP moves that work to a shared pattern. The tool is wrapped once, and any compatible assistant can use it. It also keeps AI logic in the host and access logic in the server, so API keys and sensitive access stay on the server side.
How is MCP different from an API or an automation platform?
An API is deterministic and specific: you call this endpoint with these parameters and get a defined response. MCP sits on top and lets a probabilistic model discover which tools are available and decide which to use. The API still does the actual work underneath.
An automation platform is a different layer again. As this overview of MCP and iPaaS for business leaders puts it, MCP handles access while iPaaS handles orchestration, and the two are complementary. MCP lets the assistant reach the CRM. A workflow tool still decides the sequence, the retries and the branching.
The timing matters because agents are spreading. Gartner predicts 40% of enterprise apps will feature task-specific AI agents by 2026, up from less than 5% in 2025. More agents means more connections to manage.
What do you have to get right before connecting AI to your systems?
The protocol is the easy part. A working AI agent development project spends most of its effort elsewhere. If you cannot describe the process on one page, no connection standard will fix it.
Write the process down on one page, with permissions and approvals, before any connection gets built.
Map the process first: what triggers it, what the assistant reads, what it decides, and where a person steps in. Then wire it.
Permissions and approvals
Give each tool the narrowest access that does the job. A reporting assistant gets read-only access to the tables it needs, not the whole CRM.
Put a human approval on every write action at the start: sending an email, changing a deal stage, issuing a refund. Loosen it only after you have watched the logs for a while.
Monitoring and ownership
- Logging from day one. Record every tool call, its inputs and its result, so you can answer what the assistant did and why.
- Error handling. Decide what happens when a tool times out or returns something odd: retry, stop, or hand to a person.
- Named owner. One person is responsible for the server, its credentials and its updates.
- Documentation you own. Permissions, flows and failure rules should live in your documents, not in a vendor's head.
Should you build or buy an MCP server, or wait?
Start with the cases where you need neither. If one assistant talks to one system and the flow is fixed, a direct integration is simpler and easier to debug. If your CRM or help desk vendor already ships a server, try that before writing your own.
Building makes sense when you have several internal systems, more than one assistant using them, and someone able to maintain the server. The protocol is still evolving, so maintenance is a real cost. InformationWeek's build-or-buy discussion cites an MIT report finding that 95% of generative AI pilots are failing to achieve significant business outcomes.
Waiting is a legitimate answer when the process is not mapped or no one owns it. Connecting a model to a messy process only makes the mess faster.
Where does MCP fit first in a business?
Pick a workflow that is frequent, low risk and already documented. Four realistic starting points:
Start where work is frequent and low risk, like a support inbox where a person still approves every reply.
- Support inbox. The assistant reads the customer record and past tickets, then drafts a reply for an agent to approve.
- CRM and pipeline updates. It summarizes calls and proposes field changes that a rep confirms.
- Back-office approvals. It gathers the context for a request and routes it, while the approver stays human.
- Reporting. Read-only access to a few tables, with no write risk.
Choose the one with the clearest owner and the least damage if it errs. Our operations and process automation work follows the same rule, and our client case studies show how it plays out. A readiness check helps if you are unsure.
FAQ
What does Model Context Protocol mean?
It is an open standard for connecting AI assistants to external tools and data. "Context" refers to the information and capabilities the assistant can reach, such as records, files and functions, through a common interface instead of custom integrations.
How is MCP different from an API?
An API is a fixed, specific interface to one system. MCP is a standard layer that lets a model discover and call tools, usually wrapping existing APIs. You still need the APIs, and you still need orchestration elsewhere.
Is Model Context Protocol secure for business data?
It can be, but security comes from how you set it up. MCP keeps API keys and sensitive access on the server side, away from the model. You still need narrow permissions, approvals on write actions and logging.
Closing: start with the process, not the protocol
Model context protocol for business is worth using once the process is mapped, the permissions are narrow and someone owns the result. Before that, it is a neat connector with nothing reliable to connect.
If you are not sure where you stand, take the free AI Ops Score, 12 questions on how ready your operations are for AI.